
Security and data protection for event content
Your event content
stays yours.
Hosted on AWS in Frankfurt, encrypted, and never used to train AI models. Your data and IP belong to you.
AES-256 at rest · TLS 1.3 in transit
- SOC 2 Type IIIndependent audit
- ISO 27001Certified
- GDPRCompliant
- WCAG 2.1 AAAttendee screens
- AWS FrankfurtHosting and backups
From the sound desk to their phone,
encrypted the whole way.
What happens to a session’s audio, text and translations.
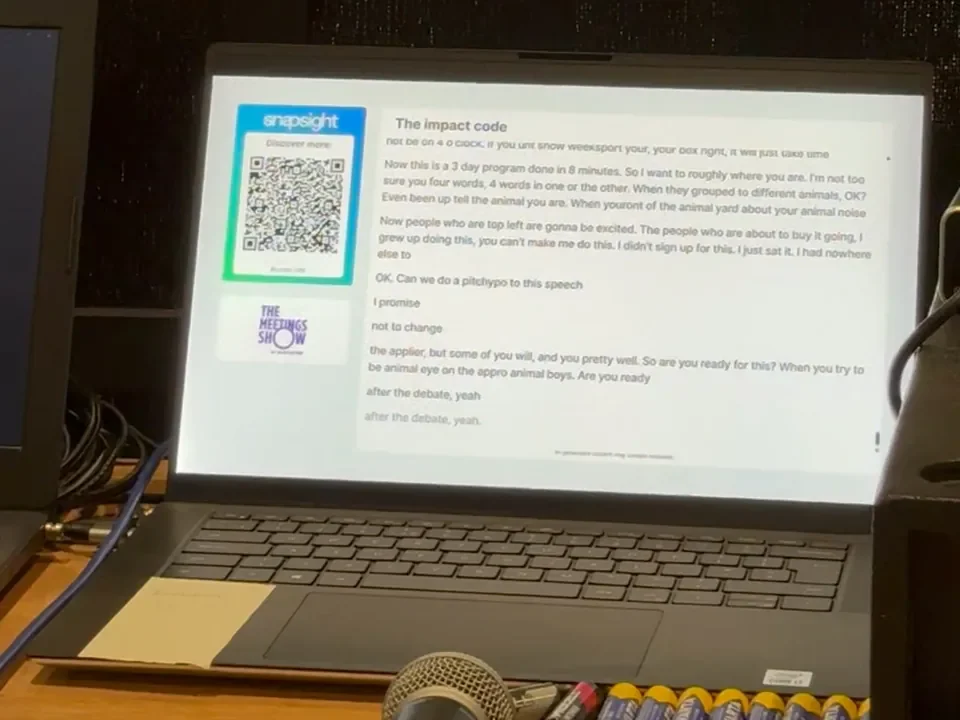
Snapsight
Hosted on AWS in Frankfurt
- Encrypted at rest with AES-256
- Backed up every day
- Never used to train AI models
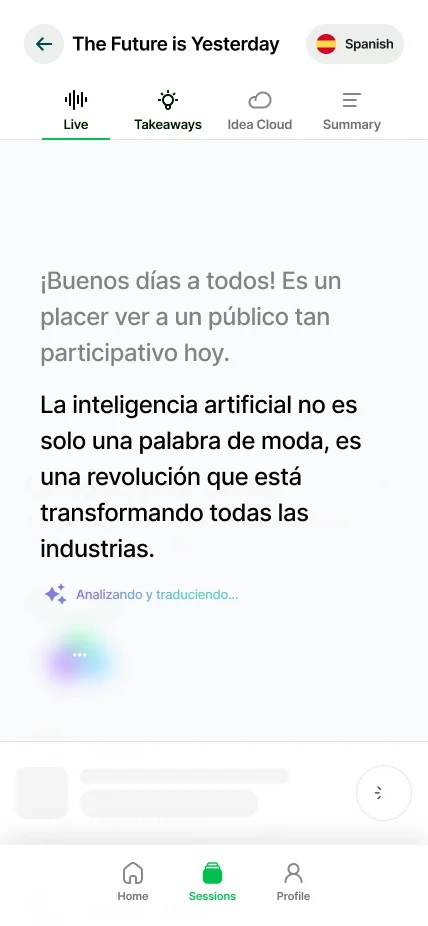
You own the transcripts, takeaways and summaries. Ask us to delete them at any time.
Real screens · Snapsight at the sound desk, The Meetings Show London 2026 · attendee view in Spanish
Every service that handles your data,
named, with where it runs.
Hosting and backups stay in AWS Frankfurt. Each service uses your data only to run Snapsight.
European Union4 services
| Company | What it does for Snapsight |
|---|---|
| Amazon Web Services | Hosting, backups and language models, in Frankfurt |
| Microsoft | Language models, in Germany |
| Imperva | Web application firewall and CDN |
| Brevo | Email marketing |
United States3 services
| Company | What it does for Snapsight |
|---|---|
| AssemblyAI | Language models |
| Google Cloud | Language models |
| Chargebee | Subscription billing, only if you subscribe through Chargebee |
As listed in our privacy policy and trust centre
Going through an IT review?
Start with our documents.
Certificates download from our trust centre. Full reports are shared under NDA.
Download now
- SOC 2 Type II letter of attestationWith GDPR and CCPA
- ISO 27001 certificateInformation security
- ISO 27017 and 27018 certificateCloud security and privacy
For GDPR, our EU representative under Article 27 is the European Data Protection Office (EDPO). Our Data Protection Officer is at dpo@snapsight.com.
Request access in the trust centreTested every year.
Backed up every day.
How often each safeguard runs, across one year.
Every day
365 times a year- Backups, managed by AWS and kept in Frankfurt
Every week
52 times a year- Vulnerability scans
Every year
Once a year- Penetration test by a CREST-certified vendor
- Business continuity and disaster recovery test
- Security and privacy training for every employee
All the time
Always on- Imperva firewall and DDoS protection
- Role-based access and audit logging
- Code testing (SAST and DAST)
- Separate development, testing and production
Enterprise controls,
set to your policies.
Available on Enterprise and on request. Tell us what you need.
- Single sign-on
- Your team signs in through your identity provider, such as Microsoft Entra ID or Okta.
- Team administration
- Manage your team’s access and roles from one account.
- Data residency
- Frankfurt by default. Other regions on request.
- Data retention
- How long content is kept, agreed with you.
- Deletion on request
- Remove any session or your whole account at any time.
- Incident notice
- We tell you as soon as possible if your data is affected.
Questions
security teams ask.
Where is Snapsight’s data hosted?
On AWS in Frankfurt, Germany, backups included. All Snapsight data moved there from AWS Singapore on 4 October 2024. Frankfurt is the default; other regions are available on request.
Do you use our sessions to train AI models?
No. Session audio, transcripts and everything generated from them are never used to train AI models, and your data, including the IP in it, belongs to you. That commitment is in Snapsight’s privacy policy, terms of use and subscription agreement, and the services it uses process your content only to run Snapsight.
Can we keep a closed session private?
Yes. Add an access code to the session, and only people with the code can open its live text and takeaways. Your content is never used to train AI models, and your data, including the IP in it, belongs to you.
Which AI providers process our sessions?
Language models from Amazon Web Services, Microsoft, Google Cloud and AssemblyAI. Snapsight’s security page lists each one with what it does and where it processes data, as its trust centre and privacy policy do.
Is our data encrypted?
Yes. All customer data on Snapsight is encrypted at rest with AES-256 and in transit with TLS 1.3.
What can we send our IT team for review?
Snapsight’s SOC 2 Type II letter of attestation (covering GDPR and CCPA), its ISO 27001 certificate and its ISO 27017 and 27018 certificate download from the trust centre now. The full SOC 2 and ISO audit reports, the latest penetration test and vulnerability assessment reports, and the data flow and network diagrams are shared under NDA: request them in the trust centre or at cs@snapsight.com.
Does Snapsight support single sign-on?
Yes, on the Enterprise plan. Your team signs in through your organisation’s identity provider, such as Microsoft Entra ID or Okta.
Can we have our content deleted?
Yes, at any time: your content is yours. Email dpo@snapsight.com to delete specific sessions or close your account, and Snapsight removes the content from its active systems. The privacy policy explains what is kept for legal reasons.
Does Snapsight run penetration tests?
Yes. Every year a CREST-certified vendor runs a vulnerability assessment and penetration test. Application penetration tests also follow any major platform update, and vulnerability scans run every week; the latest reports are shared under NDA.
Is Snapsight GDPR compliant?
Yes. For GDPR, Snapsight’s EU representative under Article 27 is the European Data Protection Office (EDPO), and its Data Protection Officer is at dpo@snapsight.com.
Bring your security questions.
We’ll go through them with you.
Book a review with our team, or start with the documents in our trust centre.